2. Installation process
To utilize AD FS technology through the DotNetNuke Platform website (and/or Evoq) you need to have “ADFS-Pro Authentication” plugin on the DNN side.
Of course on the ‘Active Directory’ side, the AD FS role nees to be installed.
2.1. Requirements
To connect DNN with ‘Active Directory Federation Services’ you need:
- Active Directory 2003 domain (or above), where Federation Services are installed and configured,
- DotNetNuke Platform (or Evoq) v7.3.4 or above,
- DNN website needs to works at the top of HTTPS protocol,
- ‘ADFS-Pro Authentication’ plugin,
2.2. Before you start
- Make all backups, including DNN database and DNN file system.
- Make sure that you have ‘host’ access to the DNN website.
- Make sure that you have ‘Administrator’ access to the Active Directory system, or access to account that allows change settings in AD FS on Active Directory.
2.3. Installation process
Sign in to the DNN website as a “DNN Host”.
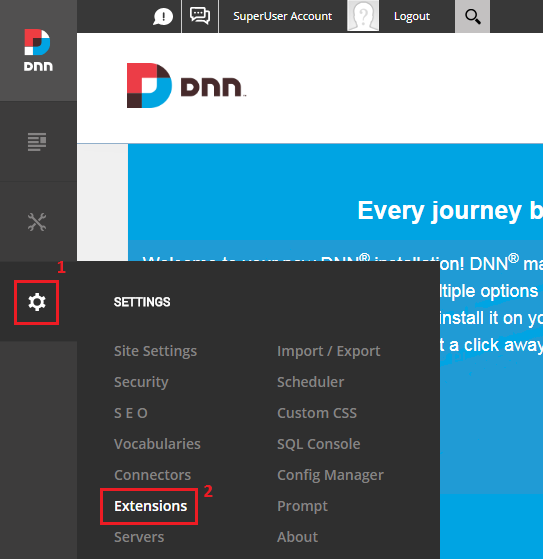
Go to “Settings-> Extensions”, see figure below.
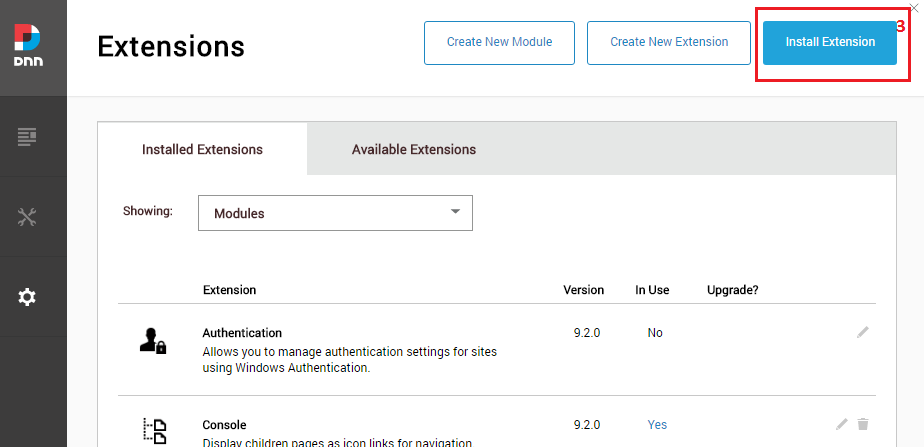
Click “Install Extension” button (top right corner) see figure below.
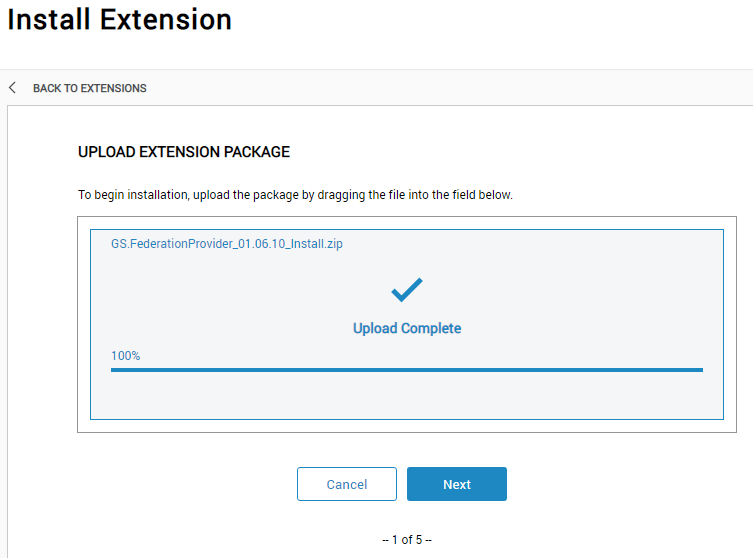
Upload extension package and click “Next” button few times. This will take you through all installation steps.
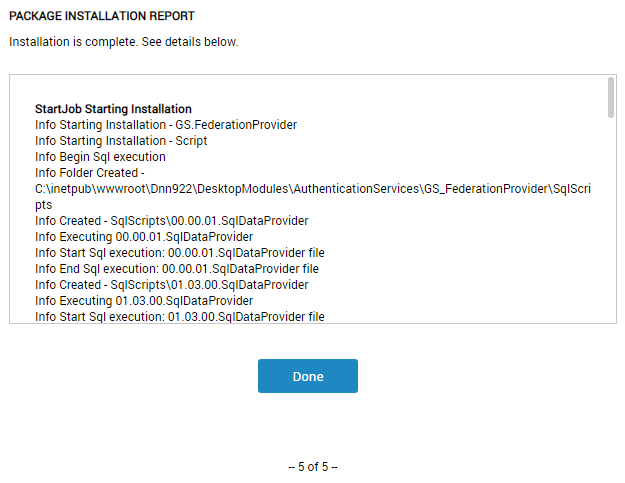
If package was successfully installed, following screen should appear. Click “Done” button to finish this process.
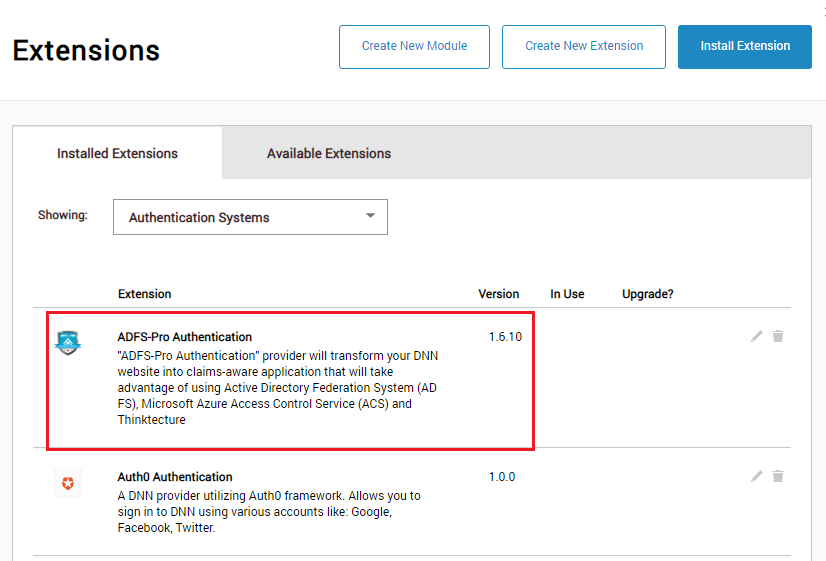
Now the ‘Installed Extensions’ section contains newly added module, the module version can be vary, see figure below.
2.4. Changes made during the module installation process
The ‘ADFS-Pro Authentication’ will add following changes to your DNN website:
In
web.configconfiguration file, in section<configuration><configSections>following entries will be added: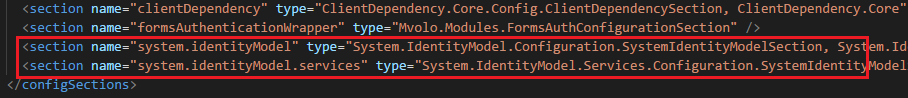
<section name="system.identityModel" type="System.IdentityModel.Configuration.SystemIdentityModelSection, System.IdentityModel, Version=4.0.0.0, Culture=neutral, PublicKeyToken=B77A5C561934E089" />
<section name="system.identityModel.services" type="System.IdentityModel.Services.Configuration.SystemIdentityModelServicesSection, System.IdentityModel.Services, Version=4.0.0.0, Culture=neutral, PublicKeyToken=B77A5C561934E089" />
In
web.configconfiguration file, in section<configuration><system.webServer><modules>following entries will be added:
<add name="CustomWSFederationAuthenticationModule" type="GS.FederationProvider.CustomWSFederationAuthenticationModule, GS.FederationProvider" preCondition="managedHandler" />
<add name="SessionAuthenticationModule" type="System.IdentityModel.Services.SessionAuthenticationModule, System.IdentityModel.Services, Version=4.0.0.0, Culture=neutral, PublicKeyToken=b77a5c561934e089" preCondition="managedHandler" />
In
web.configconfiguration file, in section<configuration><dotnetnuke><authServices><messageHandlers>following entry will be added: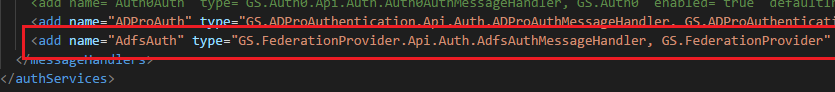
<add name="AdfsAuth" type="GS.FederationProvider.Api.Auth.AdfsAuthMessageHandler, GS.FederationProvider" enabled="true" defaultInclude="true" forceSSL="false" />
To the DNN
bindirectory following libraries are copied: